ISO — the Insurance Services Office, part of Verisk — sits quietly behind an enormous share of the property and casualty wording that insurers issue every day. Yet standardised forms, rules and endorsement libraries only become customer-facing reality when they are selected, assembled, personalised, approved, delivered and archived as actual documents, and that last mile is where many carriers, managing general agents (MGAs) and programme administrators still rely on developer tickets, consultant backlogs and manual assembly. The cost of leaving that gap unsolved is rarely dramatic; it is cumulative — slower filings-to-market, inconsistent policy packets, awkward edition management across states, provinces and regions, and a compliance team that can never quite prove which wording went out on which day.
TL;DR
- ISO provides standardised P&C policy forms, endorsements, rules and related content that insurers license and adopt; it does not issue your documents, maintain your templates or hold your audit trail.
- The real ISO-related document work happens around your core systems: form selection, schedules, declarations, endorsement packets, renewal and non-renewal notices, audit documentation and claims correspondence.
- Complexity concentrates in three places — jurisdictional variation, form edition and effective date, and data that must be drawn from several systems of record and reshaped before it can appear in a document.
- Licensed ISO material, internal research, approved production wording and the template that actually generates output are four different things, and governance should keep them distinct.
- A governed document layer such as Experlogix Document Automation can sit alongside your policy administration system (PAS), rating platform and archive — connected by API — so operations and compliance own wording and logic while IT retains control of data, identity, environments and releases.
Happy shiny people. Insurance marketing loves the image of policyholders living their best lives, blissfully unconcerned about the catastrophes their cover quietly stands behind. A centralised document layer that lets business users manage document automation accurately and quickly, without heavy ongoing IT labour, extends that same calm to the insurance professionals themselves.
What ISO Actually Provides, and Where Your Document Work Begins
ISO is an advisory and content organisation. It develops and maintains standardised policy forms, endorsements, rules and related materials for property and casualty lines, files them with regulators where required, and licenses them to insurers who adopt them in whole or in part. For many commercial and personal lines programmes, ISO content is the backbone of the policy wording, with carriers layering company-specific manuscript endorsements and proprietary coverage enhancements on top — which is exactly where ISO forms and insurance document automation meet.
What ISO does not do is run your document operation. It does not decide which endorsements apply to a particular risk in your book, assemble the policy packet, insert the schedule of locations, route the declarations page for underwriter approval, deliver the packet to the broker, file the final PDF in the archive with the right retention metadata, or write the document reference back to the policy record. That orchestration belongs to your systems — and, in practice, to a mix of your PAS, your output tooling, a few spreadsheets and some well-intentioned manual steps that nobody has had time to replace.
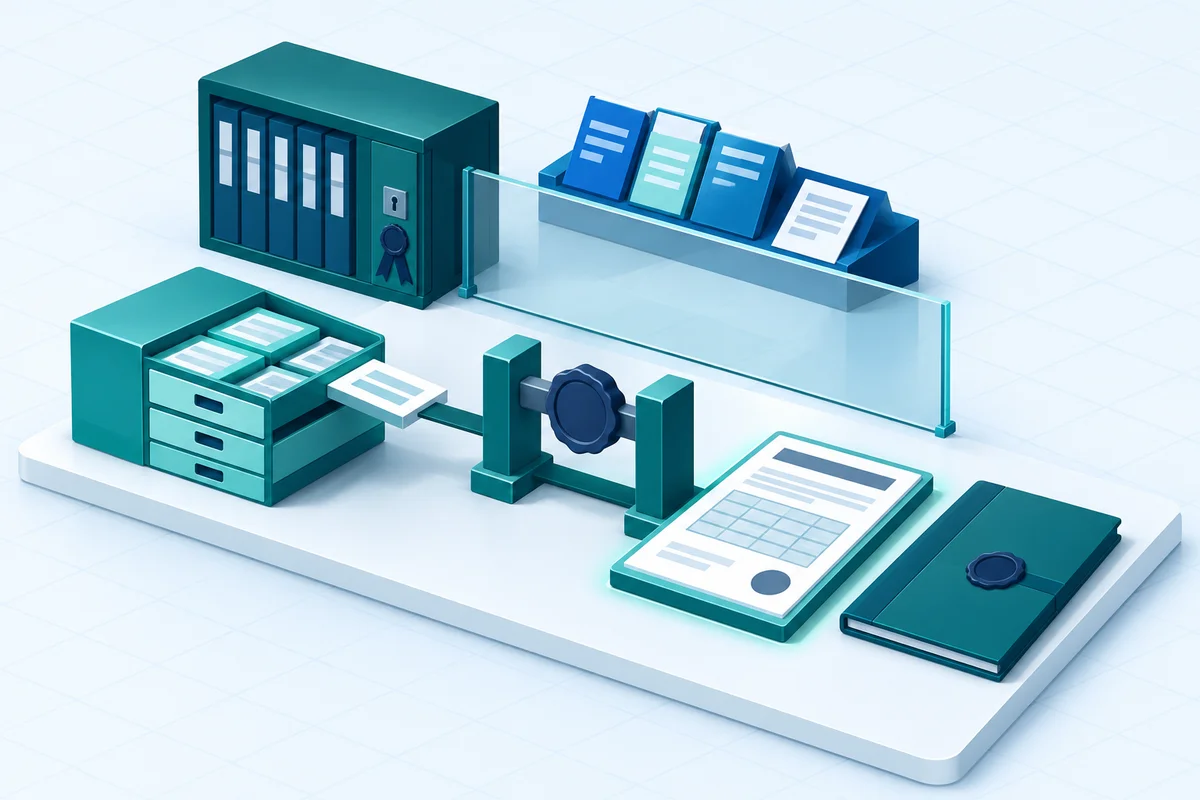
Drawing that boundary clearly is the most useful thing an insurer can do before changing any technology. ISO is the authoritative source of standardised content. Your core system is the authoritative source of policy, billing and claim state. Your document layer is where content, data, rules, approvals, delivery and evidence converge into an artefact a policyholder, broker, regulator or reinsurer will actually read.
The Document Lifecycle Around ISO-Based Policy Forms
Standardised wording touches nearly every document-producing moment in the P&C lifecycle. Mapping those moments is a practical exercise, because each one has a different trigger, a different approver and a different delivery expectation.
New business and quoting. Proposals and quote letters frequently summarise which coverage forms and endorsements will apply, long before a policy exists in the system of record. The data lives in a rating or quoting platform; the wording references forms the carrier has adopted.
Binding and policy issuance. The policy packet is the signature document of P&C insurance: declarations, the applicable coverage forms, the endorsement schedule, mandatory and state-, province- or region-specific notices, and any manuscript wording. Long commercial packets with hundreds of scheduled locations or vehicles are the stress test that exposes weak document architecture.
Endorsements. Mid-term changes generate a revised declarations page, the added or deleted endorsements with their form numbers and edition dates, and a covering explanation. Mass endorsements driven by a regulatory change can hit thousands of policies at once.
Renewals and notices. Renewal packages, premium change notices, conditional renewal notices, non-renewal and cancellation notices often carry prescribed content and prescribed timing. Timeliness here is not an operational nicety; it is frequently a regulatory requirement with evidentiary consequences.
Premium audits. Audit worksheets, audit statements and supporting correspondence draw on exposure data that may originate outside the core system entirely.
Claims correspondence. Acknowledgement letters, reservation of rights, coverage position letters and settlement documentation often quote or reference specific policy form language — and must reference the edition that was in force at the time of loss, not the current one.
Certificates, evidence of coverage and broker communications. High-volume, low-margin documents where speed and consistency matter more than creativity.
Regulatory and statutory reporting. Filing packages, statistical submissions and compliance documentation that must be reproducible on demand.
Where Complexity Emerges in ISO Forms Document Automation
Jurisdictional variation
A single commercial product may behave differently in dozens of states, provinces or regions: different mandatory notices, different amendatory endorsements, different prescribed language, sometimes different languages altogether. Teams that manage this by cloning templates per jurisdiction end up maintaining an estate that grows faster than their capacity to govern it. The more sustainable pattern is one template with jurisdiction-aware conditional content, driven by data rather than by file naming conventions.
Experlogix Document Automation’s Template Builder uses familiar Microsoft Word functionality to create policy templates with dynamic data fields pulled directly from source systems, allowing jurisdiction-specific content, dynamic tables and graphics, and automatic language selection to be embedded in a single template rather than maintained as separate versions by hand.
Form edition and effective date
This is the quiet discipline that separates a competent document operation from a fragile one. Every form carries a number and an edition date, and the correct edition is the one in force for the policy term in question. Reproducing a document two years later — for a claim, a complaint, a market conduct examination or a coverage dispute — means reproducing the edition, the data and the logic as they stood then. Design for that from the start: version templates and content blocks, stamp generated documents with the template and content versions used, and retain the data payload alongside the output.
Multi-source, multi-shape data
Documents rarely consume data as it is stored. Schedules need sorting and subtotalling. Limits need formatting and sometimes aggregating. Exposure data may sit in one system, party data in another, billing in a third, and broker detail in the agency management system. Conditional logic, filtering, calculations and lookups of this kind have traditionally been where coding and consultant hours accumulate. Moving that logic into a configurable document layer — where it can be inspected, tested and changed by the people who own the wording — is usually the single biggest reduction in ongoing development dependency.
Failure paths
Happy-path generation is easy to demonstrate and insufficient to run an operation. Decide in advance what happens when a required field is missing, when the same issuance event fires twice, when a renewal batch completes partially, when an email bounces or a portal upload fails, and when a write-back to the core system errors after the document has already been delivered. Idempotency keys, retry policies, reconciliation reports and monitoring belong in the design conversation, not the post-go-live one.
Licensed Content, Research and Approved Production Wording Are Not the Same Thing
One of the most common governance mistakes in forms-heavy operations is treating all text as interchangeable. It is worth keeping four categories distinct:
- Licensed source material — ISO forms and rules you have licensed, used in accordance with your licence terms and your adoption decisions.
- Research and interpretive content — coverage research, commentary and reference material used to inform decisions, which should never flow silently into a customer-facing document.
- Approved production wording — the clause library your legal, compliance and product teams have signed off for use, including manuscript endorsements and company-specific notices.
- Templates and generated output — the mechanism that selects and assembles approved wording, and the artefacts it produces.
No automated process should promote content from category one or two into category four without a deliberate, recorded human approval step. A content repository with structured storage, metadata, field mapping and version control — the role Experlogix Document Automation Content Manager plays — supports this by making it explicit which asset is approved, which version is current and where each one is used, so that forms adoption decisions and wording approvals leave a trail rather than living in someone’s inbox.
One template, every jurisdiction
Integration Architecture: Connecting Systems of Record to a Governed Document Layer
The architectural question is not whether systems can exchange data; it is which system owns what. A workable division of responsibility for an ISO-forms-heavy operation looks like this: the core platform owns policy, billing and claim state and raises the triggering event; the rating or quoting platform owns submission and quote data; the agency management system owns client, producer and servicing context; the document layer owns templates, clause selection logic, assembly, routing, approvals, delivery and evidence; the archive owns long-term retention; and the core system receives a write-back containing the document reference, status and delivery outcome.
API-led integration is the natural way to join these. A well-specified data contract — field names, types, nested structures, cardinality, mandatory versus optional, behaviour on schema change — is a one-time design effort that pays back every time a new product, jurisdiction or document type is added. Experlogix Document Automation provides a flexible API with features including role-based API keys and an extensive library of API calls, enabling document generation and workflow capabilities to be embedded in business applications, alongside out-of-the-box integration with platforms such as Microsoft Dynamics 365, Salesforce and NetSuite, and the ability to connect to an unlimited number of data sources. Experlogix states that its solution complies with SOC 2 and that it follows industry standards including NIST and OWASP guidance; as with any vendor claim, confirm current certifications and contractual commitments during procurement.
Practical items for the architecture review: authentication and service identity, role-based access for template authors versus approvers, network and data residency requirements, event versus scheduled versus batch triggering, synchronous generation for interactive moments and queued generation for volume, observability and alerting, environment promotion and release control, and performance testing against your genuine peaks — renewal cycles, mass endorsements and catastrophe communications, not an average Tuesday.
Business Ownership Without Losing Control
The strongest argument for a dedicated document layer in an ISO-aligned environment is organisational rather than technical. When a regulator mandates a notice change, or a new form edition is adopted, the people who understand the change are in compliance, product and operations — not in a development queue. A low-code, Word-based authoring experience lets those people make the change, route it through an approval workflow, and release it, while IT retains ownership of integrations, identity, environments and deployment gates.
This is also where the honest trade-off sits. Business ownership is not the absence of governance; it is the relocation of governance. You will need a defined template change process, named approvers, test cases for high-risk documents, a release calendar aligned to effective dates, and periodic review of the template estate. Organisations that skip this simply trade a development bottleneck for an uncontrolled template sprawl.
AI, Compliance and Human Oversight
AI is genuinely useful in document operations — and genuinely sensitive in regulated ones. The defensible pattern keeps AI in assistive and orchestrating roles: suggesting template structure, helping configure a workflow, drafting non-prescribed narrative sections for human review, summarising a long packet for an internal reviewer, or responding to a business user's request to initiate a document workflow. The pattern to avoid is AI exercising judgement on coverage, pricing, eligibility, underwriting or claim outcomes, or improvising policy wording where prescribed language applies.
Experlogix describes an MCP (Model Context Protocol) server for Smart Flows that allows AI agents to connect to existing systems in a structured, auditable way, with documents generated through Experlogix remaining traceable and agent actions logged, operating within parameters the organisation defines rather than as a black box. The principle generalises: an AI agent should be able to invoke a governed workflow, but the workflow — approved templates, approved clauses, mandated approvals, delivery rules, retention — should be what actually determines the output. Productivity is the benefit; supervision, auditability and business control are the conditions.
Architectural Trade-Offs Worth Debating Openly
Most core platforms, output tools and forms libraries already produce documents, and many insurers run them well. The question is not whether native capability exists but where each document type is best served.
Documents that are tightly coupled to a single system's data and change rarely often belong where they are. Documents that span multiple systems, vary heavily by jurisdiction and product, change frequently under regulatory pressure, demand business-user maintenance, or need orchestration across approval, e-signature, delivery and archive tend to justify a dedicated, centralised document layer. Many organisations end up with both, deliberately — and that is a legitimate architecture, provided the boundary is documented rather than accidental.
Centralising also creates an option that is easy to overlook: one governed template estate serving several platforms at once. Carriers running more than one core system, or an acquired book on a legacy platform alongside a modern one, frequently find that a shared document layer is the cheapest route to consistent branding, consistent notices and consistent evidence across the whole portfolio.
Be candid about the counterweights too. A centralised layer introduces another release process and another set of dependencies to monitor. It is worth it when document variability and change frequency are high; it is overhead when they are not.
Summary
ISO supplies standardised forms, rules and content that shape a great deal of P&C policy language, but the operational burden of producing, approving, delivering, archiving and reproducing documents remains firmly with the insurer. The complexity that matters is concentrated in jurisdictional variation, form edition and effective-date fidelity, multi-source data that must be reshaped before it can appear in a document, and the failure paths that only surface at volume.
A sensible next step is not a technology decision at all. Map your document types against the lifecycle stages above, and for each one record the source of truth, the trigger owner, the template owner, the approver, the delivery channel, the archive and the write-back. Then identify the documents that are expensive to change, jurisdiction-sensitive or dependent on more than one system — those are the candidates for a governed document layer. Keep licensed source material, research, approved wording and production templates clearly separated, insist that every generated document can prove which template, content version, data and approval produced it, and decide deliberately which AI assistance you want inside those guardrails. Get that map right, and the subsequent platform conversation — whether it involves Experlogix Document Automation or anything else — becomes a much shorter and much better-informed one.
Veelgestelde vragen
What role does ISO Forms play, and where does document production begin?
ISO is an advisory and content organisation. It develops and maintains standardised policy forms, endorsements, rules and related materials for property and casualty lines, files them with regulators where required, and licenses them to insurers who adopt them in whole or in part.
Where does insurance document complexity arise around ISO Forms?
A single commercial product may behave differently in dozens of states, provinces or regions: different mandatory notices, different amendatory endorsements, different prescribed language, sometimes different languages altogether. Teams that manage this by cloning templates per jurisdiction end up maintaining an estate that grows faster than their capacity to govern it.
How should licensed insurance content be handled before document production?
One of the most common governance mistakes in forms-heavy operations is treating all text as interchangeable. It is worth keeping four categories distinct: Licensed source material — ISO forms and rules you have licensed, used in accordance with your licence terms and your adoption decisions.
How should a governed document layer connect with ISO Forms?
The architectural question is not whether systems can exchange data; it is which system owns what.
Who should own document templates, approvals and governed changes?
The strongest argument for a dedicated document layer in an ISO-aligned environment is organisational rather than technical. When a regulator mandates a notice change, or a new form edition is adopted, the people who understand the change are in compliance, product and operations — not in a development queue.