OneShield is a configurable property and casualty (P&C) core platform family. It covers policy administration, billing and claims for carriers, managing general agents (MGAs), programme administrators and specialty writers. The record-keeping is rarely the hard part. The hard part, and the real subject of OneShield document automation, is everything that has to be produced around it: policy packets, declarations pages, endorsement schedules, invoices and lapse notices, claims correspondence, producer packets and regulatory filings. Each one depends on jurisdiction, product, form edition and effective date. When that document layer is pieced together from templates in several places, scripted output logic and a queue of change requests to IT or implementation consultants, a one-line wording change can take weeks rather than an afternoon.
TL;DR
- OneShield document automation works best when OneShield remains the system of record for policy, billing and claims transactions and a dedicated document layer handles template governance, multi-source assembly, approvals, delivery and evidence around it.
- Document complexity in a OneShield estate is rarely about layout. It comes from variations by jurisdiction and region, product-specific wording, effective-dated form editions, nested schedules and data that lives in several systems at once.
- API-driven integration lets a OneShield event trigger a governed document workflow with the latest data from each relevant source. That event might be a quote issued, a policy bound, an endorsement processed, a claim status change or an invoice raised.
- Experlogix Document Automation is deployed alongside core platforms rather than instead of them. It provides a template builder that works like Microsoft Word, a drag-and-drop workflow builder, Smart Forms for data capture and Content Manager for assets and version control. It also has plug-and-play connections to eSignature platforms, including DocuSign, Adobe Acrobat Sign, OneSpan Sign, Sertifi and ConsignO Cloud.
- AI can help gather inputs and start governed document workflows through capabilities such as the Experlogix Smart Flows MCP server. Regulated judgement, approvals and audit trails stay with people and authorised systems.
Happy shiny people. Insurance marketing loves the image of the policyholder living their best life, untroubled by the catastrophes their cover quietly stands behind. A centralised document layer that lets the business manage its own templates, rules and workflows accurately and quickly, without a standing queue of IT work, lets the insurance professionals behind that policy live their best lives too.
What OneShield Owns, and What the Document Layer Owns
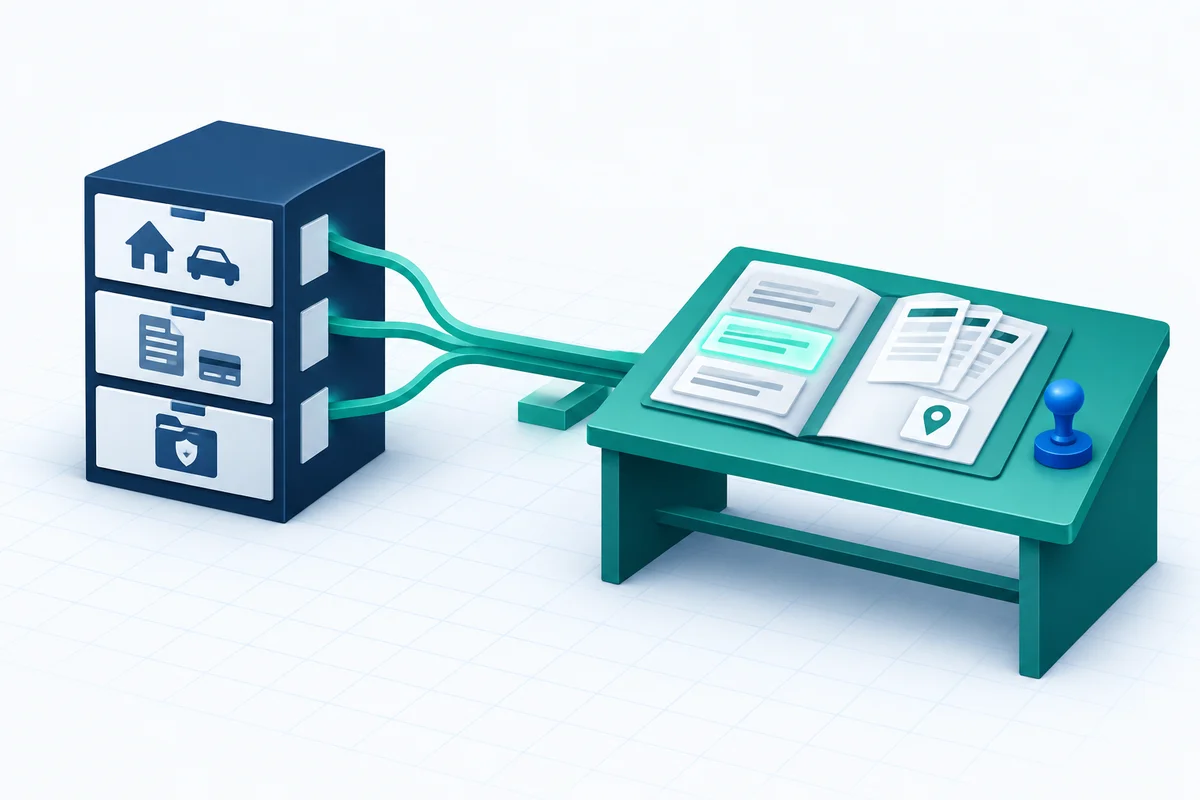
OneShield’s role in a carrier or MGA architecture is to administer the insurance transaction. That includes product definitions, rating and underwriting configuration, policy lifecycle events, billing schedules and receivables, claim files, reserves and payments. It holds the authoritative record of what the policy says, what is owed and what is happening on a claim.
A document layer answers a different set of questions. Which document must exist because of this transaction? Which approved wording and form edition applies for this jurisdiction, product and effective date? Who must approve it before it goes out? Which channel does it go through, and what proves it was sent?
Keeping that distinction clear is the most useful architectural decision an insurer can make here. In practice, it means agreeing in writing who owns each of the following:
- Source of truth for policy, billing and claim data: OneShield, with supporting data from CRM, document management or actuarial systems where relevant.
- Trigger: which OneShield event or scheduled job starts generation.
- Template and clause content: usually operations, product and compliance teams, not IT.
- Approval: named roles, with thresholds for which documents need human review.
- Delivery: email, print, portal, broker channel or eSignature.
- Archive and retention: the enterprise content system of record.
- Write-back: which reference, status or link returns to the OneShield record.
Many OneShield implementations already produce documents natively, and that capability is not in question. The practical question is narrower: which documents justify a dedicated, business-maintained layer because of their variability, approval burden, multi-system data needs or volume?
Where Document Complexity Actually Emerges
Ask a OneShield operations team where the document pain is, and the answer is almost never “the layout”. It is the conditional logic.
Jurisdictional variation. Mandatory notices, cancellation timeframes, fraud warnings and disclosure wording differ by state, province and region. A template estate with one variant per jurisdiction multiplies quickly. One that encodes jurisdiction as a rule stays manageable. Configurable business rules that apply jurisdiction-specific language and disclosures remove most of the guesswork and the need to maintain separate template versions by hand.
Form editions and effective dates. Reproducing a document two years after issue means reproducing the form edition and wording that applied then, not the current one. Effective-dated content and version control are compliance requirements, not conveniences.
Product-specific structure. A commercial package policy with location schedules, vehicle schedules and a long list of endorsements is a different assembly problem from a monoline personal auto declaration. Nested and structured data has to be unpacked, filtered, totalled and sometimes recalculated before it can appear in a document. Historically, that work has fallen to developers.
Data from more than one place. A declarations page may need data from several sources:
- the policy transaction from OneShield
- producer and client servicing context from an agency or CRM system
- a licensed form reference from a content provider
- brand assets from a central repository
Enterprise-grade document automation is built to connect with existing systems, CRMs, ERPs and databases. It pulls current data so that every document starts from accurate information rather than copy-and-paste.
Volume shape. Renewal cycles, mass endorsements after a rate or form change, and catastrophe communications are not steady-state workloads. They are peaks. Without idempotent triggers, retry handling, partial-batch reconciliation and monitoring, a large renewal run becomes a manual reconciliation exercise.
Document Touchpoints Across the OneShield Lifecycle
Mapping documents by lifecycle stage is the fastest way to size the opportunity. A typical P&C estate running OneShield produces:
| Submission and quote | Application packets, supplementary questionnaires, quote letters and proposals, subjectivity letters. |
|---|---|
| Bind and issuance | Binders, declarations pages, policy packets with forms and endorsements, certificates and evidence of coverage, ID cards, producer confirmations. |
| Mid-term | Endorsement packets and revised declarations, premium-bearing change notices, underwriting information requests, inspection and loss-control correspondence. |
| Billing | Invoices and instalment schedules, premium increase notices, past-due reminders, cancellation and reinstatement notices, lapse warnings. |
| Renewal | Renewal offers and packets, non-renewal notices, rate-change disclosures, renewal questionnaires. |
| Claims | Acknowledgement letters, reservation of rights, coverage position letters, status updates, settlement and release documents, payment advices, closure letters. |
| Audit and compliance | Premium audit requests and results, statutory and regulatory notices, state, provincial and regional filing packages, complaint-handling correspondence. |
| Distribution | Producer onboarding and appointment documents, commission statements, agency communications. |
Each of these has its own mix of trigger, data source, approval requirement and channel. An honest list, including the documents that work well as native output, is a better starting point than an abstract platform-level decision.
One OneShield event, one governed document
OneShield Document Automation Architecture: Treating Documents as a Service
The pattern that works well around a core platform runs in this order:
API-led integration carries that pattern. Experlogix Document Automation provides a flexible API with role-based API keys and an extensive library of API calls, so other applications can call document generation and workflow execution as a service.
- OneShield event
- Validated trigger
- Governed data retrieval
- Rules and template selection
- Assembly
- Approval or signature
- Delivery
- Archive
- Write-back
The integration is a one-time setup: mapping the data contract, authentication and the events that matter. AI assistance can help shape and speed up that configuration work. Once in place, the same interface supports one declarations page generated interactively and a renewal batch run overnight. It also stays the same when a second core system, an agency platform or a legacy book joins the estate.
A few design points are worth settling early:
- Data contract. Define required fields, optional fields, nested structures and what happens when values are missing. Decide whether a missing field blocks generation, uses a default or goes to exception review.
- Identity and access. Use service identities for system-to-system calls and role-based access for people, with logging on both.
- Idempotency. Duplicate events happen. Agree on a transaction key so a reissued endorsement event does not produce two packets.
- Failure paths. Plan for retries, dead-letter handling, partial-batch reconciliation, delivery failures and rollback. Design these before the first renewal peak, not after.
- Observability. Provide execution status, document traceability and reconciliation reporting that operations staff can read without a developer.
The surrounding ecosystem fits naturally here:
- Microsoft Power Automate or ServiceNow for broader orchestration
- Dynamics 365 or Salesforce for client and producer context
- SharePoint, OpenText or Hyland for archive
- eSignature platforms for execution, with plug-and-play connections to DocuSign, Adobe Acrobat Sign, OneSpan Sign, Sertifi and ConsignO Cloud covering generation, signature and storage in one continuous flow
Business Ownership Without Losing Control
The biggest benefit of a dedicated document layer is not technical. It is about who controls the wording.
Experlogix's template builder uses the same functionality as Microsoft Word. Business users can build templates with dynamic data fields, conditional content, dynamic tables, graphics and language variations without coding and without leaving familiar software. Workflows are built in a visual drag-and-drop builder designed for non-technical users.
Smart Forms are web-based forms that collect data as part of an automated workflow. They help when the data you need is not yet in a system: a workflow can email a link to a form, and completing the form can trigger the next document. Content Manager is a secure, structured repository for PDF forms, documents, logos, images and multimedia, with linked metadata forms, field mapping and version control.
Governance does not loosen as a result. It becomes easier to follow. Template version control keeps teams on approved formats. Audit trails record edits, approvals and timestamps, creating a reviewable record of what was generated, from which template, by whom and when.
The division of labour that works:
- IT and security own integration, environments, identity and release control.
- Operations and compliance own wording, templates and approvals.
- Product owns decisions about jurisdiction, form edition and effective date.
IT sets it up once, and then the business runs it.
AI, Supervision and Governed Workflows
AI is most useful in insurance documents where its role is least dramatic: assembling inputs, drafting within approved content, flagging inconsistencies and speeding up configuration, all within existing governance.
The aim is AI that starts a governed workflow, not AI that decides an outcome. The Experlogix Smart Flows MCP server is a Model Context Protocol (MCP) server available for use in Microsoft Copilot Studio. It lets Copilot agents:
- discover which Smart Flows exist
- query the inputs each one requires
- ask follow-up questions when information is missing
- trigger execution
- retrieve execution status and generated documents
The automation logic stays in Smart Flows rather than inside the agent. Every execution runs within the same security and permissions framework already in place, with the same logging and visibility. Administrators can monitor execution status, inspect results and trace generated documents with familiar tools, even when a flow was triggered conversationally.
Here is an illustrative example in a OneShield estate. A claims handler asks an internal agent to prepare a coverage position letter for a claim. The agent gathers and confirms the required inputs, then calls a governed flow. That flow retrieves current claim and policy data, selects the approved template and the wording for the jurisdiction, and assembles the letter. It then routes the letter for the required human approval, delivers it and records the evidence. Coverage, pricing, eligibility and claim decisions stay with authorised people and systems. The agent handled the conversation; the document layer handled the control.
Summary
OneShield administers the policy, billing and claims transaction. The document layer around it decides:
- what gets produced
- which approved wording applies
- which jurisdiction and form edition apply
- who approves it
- how it is delivered
- what evidence proves it was sent
Keeping those responsibilities separate, rather than letting document logic build up inside configuration and custom code, keeps a wording change an operational task rather than a project.
A reasonable next step is small and concrete. List the documents your OneShield processes generate across the lifecycle. For each one, record the trigger, data sources, approval requirement, delivery channel, retention rule and who currently makes changes. Focus first on documents where changes still go to "IT" or "consultant" and where variation by jurisdiction, product or effective date is high. These have the clearest case for a governed, business-maintained document layer.
Combining native core-platform output with a dedicated document automation platform is one architectural option among several. Judge it against your own document inventory, change frequency and peak volumes, all of which you can measure before anyone writes integration code.
Veelgestelde vragen
What role does OneShield play, and where does document production begin?
OneShield's role in a carrier or MGA architecture is to administer the insurance transaction. That includes product definitions, rating and underwriting configuration, policy lifecycle events, billing schedules and receivables, claim files, reserves and payments. It holds the authoritative record of what the policy says, what is owed and what is happening on a claim.
Where does insurance document complexity arise around OneShield?
Ask a OneShield operations team where the document pain is, and the answer is almost never "the layout". It is the conditional logic. Jurisdictional variation. Mandatory notices, cancellation timeframes, fraud warnings and disclosure wording differ by state, province and region. A template estate with one variant per jurisdiction multiplies quickly.
Which document workflows extend around OneShield?
Mapping documents by lifecycle stage is the fastest way to size the opportunity. A typical P&C estate running OneShield produces: Each of these has its own mix of trigger, data source, approval requirement and channel. An honest list, including the documents that work well as native output, is a better starting point than an abstract platform-level decision.
What should a governed document architecture around OneShield include?
The pattern that works well around a core platform runs in this order: API-led integration carries that pattern. Experlogix Document Automation provides a flexible API with role-based API keys and an extensive library of API calls , so other applications can call document generation and workflow execution as a service.
Who should own document templates, approvals and governed changes?
The biggest benefit of a dedicated document layer is not technical. It is about who controls the wording. Experlogix's template builder uses the same functionality as Microsoft Word . Business users can build templates with dynamic data fields, conditional content, dynamic tables, graphics and language variations without coding and without leaving familiar software.